

Cybersecurity · Level 3
Tailored cybersecurity assessment with certificate
Assess the security risks that matter to your business, with a report and certificate.
Define the systems and risks with us, then receive a tailored security assessment, a practical remediation plan and a walkthrough for your team.
$1,500USD · one-time service fee
- No account needed to pay
- Fixed price, paid once
- Delivery: Planned with you in the scoping session
What you walk away with
The certificate records completed assessment work; it does not certify the system as vulnerability-free or establish accredited compliance.
Assessment built around your business
Agreed systems, risks & testing objectives.
Detailed findings & team walkthrough
Evidence, attack paths & a remediation plan.
EWC certificate of assessment
Documented scope, assessment dates & report reference.
The scope
Everything that’s included.
Scoping session to define business risks, authorized systems and assessment objectives
Manual security assessment and controlled testing across the agreed websites, applications and APIs
Authentication, permissions, data exposure and business-logic checks within the agreed coverage
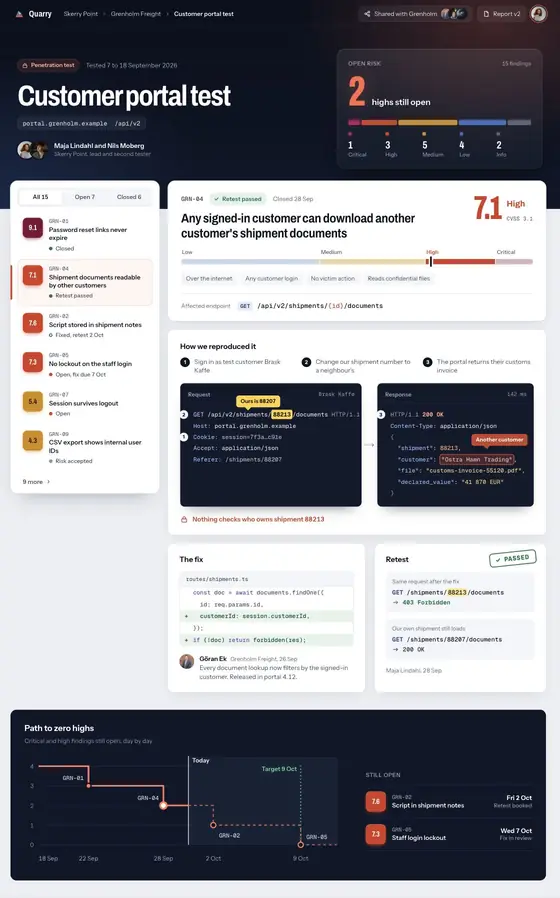
Detailed report with evidence, severity, attack paths and a prioritized remediation plan
Findings walkthrough with your team
EWC -issued certificate of assessment recording the assessed scope, dates, methods and report reference
A good fit if
You need an assessment tailored to your systems and a documented record of the work completed.
What we need from you
- Business goals, system inventory and priority risks
- Written target-owner authorization, agreed coverage and rules of engagement
- Approved testing window, stop contact, data-handling limits and any agreed test accounts
Delivery
Planned with you in the scoping session.
Not included
- Accredited compliance certification, regulatory approval or a guarantee of complete security
- Destructive testing, denial-of-service, social engineering and unauthorized third-party assets
- Remediation implementation, retesting and ongoing monitoring unless separately agreed
Tailored cybersecurity assessment with certificate$1,500one time
